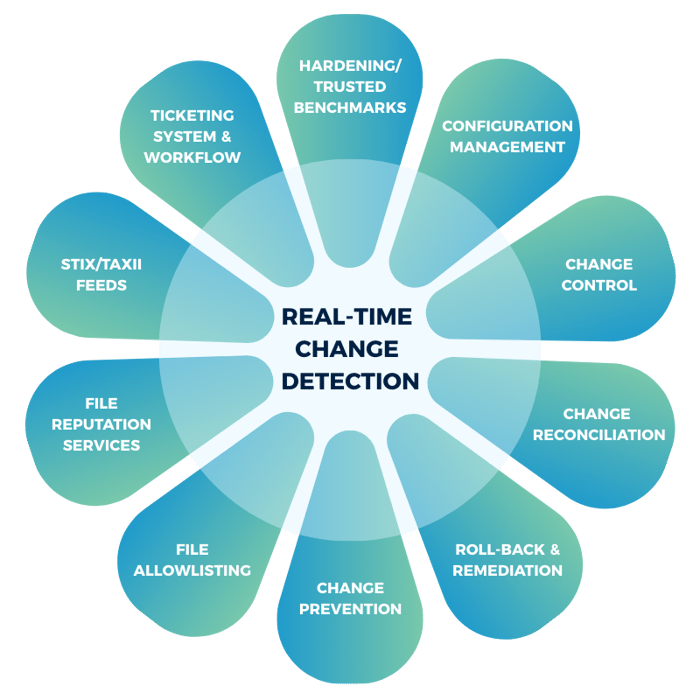
FIM software works in four stages:
1. Baseline. CimTrak captures a trusted hash and metadata snapshot of every critical file, registry key, and configuration setting.
2. Monitor. Changes are watched in real time rather than on a scheduled scan.
3. Compare. Every change is checked against the baseline; known-good patterns can reconcile automatically.
4. Alert & remediate. Unauthorized changes trigger a detailed alert and can be rolled back in one click.
Two reasons come up most often:
Requirements 11.5.2 and 10.3.4 call for change-detection mechanisms, like file integrity monitoring, on critical files and audit logs, with critical file comparisons at least weekly.
The Security Rule requires safeguards against improper alteration or destruction of ePHI (45 CFR 164.312(c)) and audit controls that record system activity (164.312(b)). FIM is a common way to meet both.
Section 404 requires effective internal controls over financial reporting. Auditors typically test change management on financial systems, and FIM provides evidence that unauthorized changes are detected.
CIP-010 requires a documented configuration baseline for BES Cyber Systems and, for high-impact systems, monitoring for changes to that baseline at least every 35 days.
Control SI-7 calls for integrity verification tools to detect unauthorized changes to software, firmware, and information. It's part of the moderate and high baselines federal agencies follow under FISMA.
Explore the 50+ compliance requirements CimTrak helps with.
for servers, endpoints, and workstations where deep, real-time file-system-level detection is needed.
for network devices, hypervisors, and systems where installing an agent isn't practical.
Changes are caught as they happen instead of reconstructed later from logs, which can be incomplete, delayed, or tampered with.
Most FIM tools stop at alerting. CimTrak can reconcile known-good changes automatically and roll back unauthorized ones.
Antivirus software looks for known malicious code signatures. File integrity monitoring doesn't care what caused a change. It detects any unauthorized modification to a file, configuration, or setting, regardless of whether malware, a misconfigured script, or a person caused it. Many security teams run both, since they catch different things.
Traditional FIM tools scan on a schedule (hourly, daily), which leaves a detection gap. CimTrak monitors continuously in real time, so changes are flagged as they happen rather than at the next scheduled scan.
A well-built FIM tool has minimal performance impact because it monitors file-system events directly rather than performing full disk scans repeatedly. Ask any vendor for their specific resource footprint benchmarks before deploying at scale.
Yes. This is one of FIM's biggest advantages over signature-based tools. Because FIM detects any unauthorized change rather than matching against known threat signatures, it can flag zero-day exploitation even before a signature exists for it.
They're related but distinct. Configuration management defines what a system's settings should be. File integrity monitoring verifies what they actually are right now and alerts on drift from that baseline. CimTrak combines both by maintaining the trusted baseline and monitoring against it continuously.
Few regulations require FIM by name. PCI DSS is the clearest case: any organization that stores, processes, or transmits payment card data must deploy change detection on critical files, and the standard cites file integrity monitoring as the example. Energy utilities subject to NERC CIP and federal agencies following NIST SP 800-53 must also detect unauthorized file and configuration changes. In healthcare (HIPAA) and at public companies (SOX), FIM isn't mandated, but it's one of the most common ways to show auditors that integrity and change controls are working. Many organizations outside these sectors also adopt it as a security best practice.